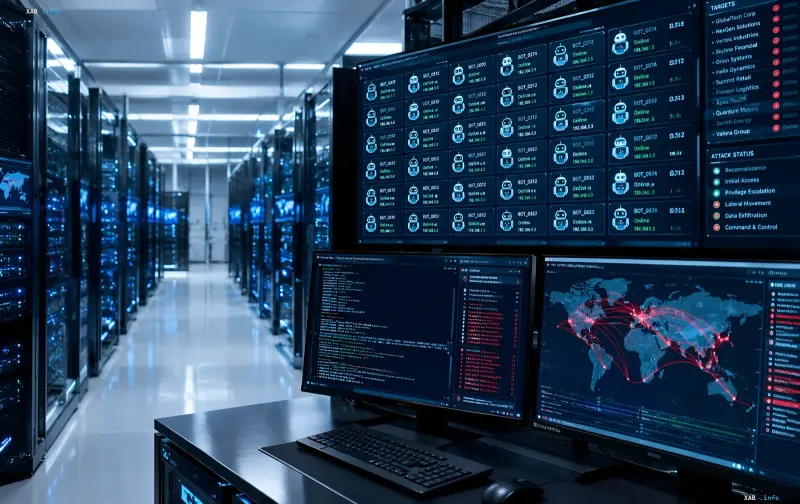
Cybercriminals have moved to a new level of automation: according to a report by the Google Threat Intelligence Group (GTIG), attackers are no longer limited to ad-hoc requests to neural networks but are building entire "teams" of AI assistants capable of independently performing individual stages of an exploit. As reported by RBC-Ukraine with reference to the study, such systems allow for attacks to be carried out significantly faster and on a much larger scale, turning intrusions into a process similar to mass production.
From Manual Prompts to Autonomous AI "Teams"
Google notes that criminals are moving away from manual prompting and are using open-source security testing systems—specifically ARTEX, CAIRN, CyberStrikeAI, HexStrike AI, and PentAGI. These tools combine language models with dozens of cyber reconnaissance utilities, thereby automating the entire intrusion cycle: from information gathering to vulnerability exploitation. The high speed of such systems leaves noticeable digital footprints, yet their capabilities continue to grow, posing serious challenges for developers and security specialists.
Who vs. Whom: From Financial Hackers to State Actors
According to the report, such tools are used both by financially motivated hackers and groups linked to the governments of specific countries, including China. For instance, the CAIRN system was detected during cyberattacks on American aerospace companies, and a modified version of PentAGI was used against organizations in Asia. GTIG also documented an autonomous system, exploit_agent, on a public server for the first time; it independently analyzed web application code, wrote exploits, and launched them against French media, entertainment, and educational websites.
Accelerating Attacks and Shrinking the "Vulnerability Window"
AI now helps hackers quickly analyze third-party code before and after updates are released: this allows them to instantly find patched bugs, create exploits, and attack unprotected servers before administrators have time to install patches. The report notes that between January and August 2026, the number of exploited vulnerabilities nearly doubled. In August, hackers exploited two zero-day vulnerabilities in PaperCut servers: with the help of AI, a mass attack on hundreds of companies was launched just four days after the information was disclosed, and gaining domain administrator rights took mere minutes.
AI in Information Operations
State entities and political monetization networks, according to researchers, have fully integrated AI into their operations: language models help create realistic profiles, generate content, and automate promotion. In August, investigators exposed an information operations platform targeting Europe and the Middle East that mimicked local dialects with intentional errors and generated artificial camera defects for photos to bypass social media protection. Another contractor was reportedly developing software to manage more than 100,000 fake accounts via cloud-based virtual smartphone farms, where neural networks "warmed up" new profiles by simulating normal user behavior before starting political agitation.
LLMJacking: Theft of Computing Power
Due to the high cost of computing, hackers have started mass-stealing corporate credentials and API keys for free access to cloud resources—a scheme dubbed LLMJacking. In some cases, according to the report, company losses exceeded $100,000 per day, reaching a total of $1 million. Criminals monetize the gained access through underground LLM Mixer platforms: on darknet forums, they sell access to advanced and uncensored models for prices ranging from $0.10 to $25 per million tokens.
At the same time, GTIG points out a side effect of automation: there has been an increase in non-functional exploits created using neural networks, which forces security professionals to spend extra time verifying them. Together, these trends indicate that AI is becoming more than just a speed-up tool; it is a structural element of modern cybercrime, ranging from infrastructure attacks to information operations and the economy of shadow computing resources.