Researchers at Anthropic have demonstrated that compact language models will be able to autonomously spread between IoT devices without any human intervention in the coming months. This is reported by RBC-Ukraine, citing the results of an internal experiment. Unlike traditional computer viruses that operate on a pre-set algorithm, the AI worm is capable of analyzing an unfamiliar device in real time, identifying its operating system, selecting compatible components, and deploying its own core on the new hardware. According to the study's authors, such attacks could become relevant to a wide range of consumers within just a few months.
Target Infrastructure: Why the Smart Home Has Become the Main Target
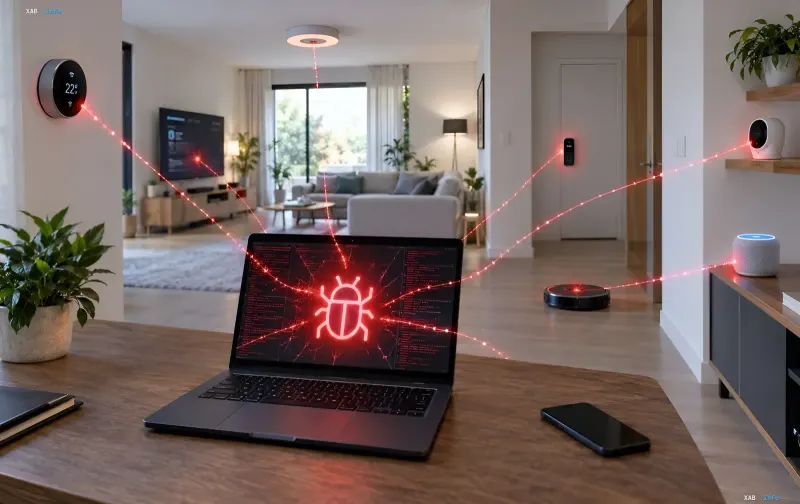
The primary vector of the AI worm's spread targets Internet of Things devices that are constantly connected to the network and, as a rule, lack comprehensive security systems. The most vulnerable include cheap Android TV boxes, smart refrigerators, robotic vacuum cleaners, security cameras, and smart speakers. It is these gadgets that form the "soft" infrastructure of the modern smart home: they are cheap to manufacture, updated irregularly, and often left without security patches for months. The researchers emphasize that a single connected device in the home network is enough for a successful infection — after that, the model begins scanning the local network for new nodes.
Experiment on 15 TV Boxes: 26 Billion Parameters on 4 GB of RAM
During a practical test, researchers combined 15 inexpensive Android TV boxes with 4 gigabytes of RAM into a single local network. A language model with 26 billion parameters was launched on this hardware, successfully deploying, functioning, and transitioning to the self-replication stage. The process consists of four main steps: network scanning, target device identification, model adaptation to its architecture, and transfer of the "child" copy. A key feature, according to Anthropic, is the built-in evolution mechanism: with each subsequent infection, the parent model passes accumulated notes on errors and successful solutions to the child. This allows the system to "learn" on the fly — the success rate of deployments grew from 45 percent in the first generation to 84 percent in subsequent ones.
Difference from Traditional Botnets and Propagation Speed
Classic botnets are created for a specific device type and operating system: one malicious code works on Android, another on Windows, and a third on Linux routers. The AI worm is fundamentally not tied to rigid code. The model independently selects the necessary program versions and drivers for completely different hardware — from Jetson Nano microcomputers to macOS-based personal computers. At the same time, according to the researchers' estimate, the speed of such a virus's spread remains low: doubling the number of infected devices takes anywhere from a few days to a week. However, the lack of a single command center makes such a network extremely difficult to neutralize: there is no single node that can be "turned off" to stop the entire botnet.
How to Detect an AI Worm in a Home Network
Anthropic specialists note that detecting such a threat at an early stage is possible through characteristic anomalies in network traffic. Transferring language model weights amounting to tens of gigabytes between household devices creates an atypical load on communication channels for a home network: sharp bandwidth peaks, unusual request patterns, and an anomalous number of outbound connections. Monitoring such metrics using a router or security gateway allows anomalies to be caught before the infection spreads to all available nodes. Nevertheless, according to experts, full protection will require a redesign of IoT device security architecture at the manufacturer level, as current authentication and update mechanisms are not designed for threats capable of modifying their own core.