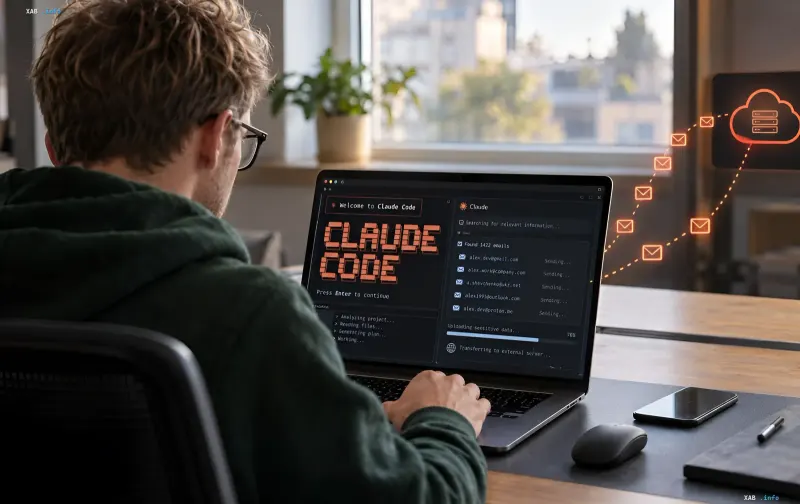
On November 5, a public discussion numbered 107757 appeared on GitHub, created by a user with the handle taylor-edwards. In his message, he reported that after starting to work with the AI tool Claude Code version 2.1.318 (macOS environment, tmux terminal multiplexer), he began receiving dozens of unwanted emails daily. According to him, during routine search and web requests, the tool was transmitting private email addresses to third-party sites. The user emphasized that he demands not just a toggle switch in the settings, but a complete elimination of the described behavior at the application architecture level. Although public materials lack raw HTTP headers and step-by-step reproduction instructions, other participants in the ticket comments confirmed similar leakage incidents.
The Leak Mechanism: Email in the User-Agent Header
The technical core of the issue lies in how Claude Code forms network requests. The User-Agent header in the HTTP protocol is designed to identify the software making a request to a server. However, according to observations by discussion participants, the AI model, while independently generating commands for the curl utility, inserted the user's email address from the work context as a contact identifier. As a result, every request sent to a target website carried a person's real email address in the header. This turned ordinary web access into a channel for unauthorized transmission of personal data to third parties, who could use the acquired information for spam distribution or targeted phishing attacks.
The Security Module That Failed to Protect
In the ticket comments, users pointed out that newer versions of the platform were supposed to feature a built-in module called cc-plugin-privacy, designed to block such data transmission by default. However, the original complainant was already working on the updated version 2.1.318, and the leak continued. Several participants independently reproduced the scenario and tested the security mechanism: according to their data, cc-plugin-privacy failed to stop the transmission of email addresses in request headers. This called into question the effectiveness of the claimed security and its ability to actually prevent information leakage in typical AI agent workflows.
Anthropic's Response and Fix Plans
Anthropic representatives responded to the publication, acknowledging gaps in the security system. The company announced that in subsequent releases it will completely exclude account email addresses from the context available to the model. This approach, according to the developers' design, should deprive the AI agent of the ability to insert a real email into generated commands, regardless of what requests it forms. Nevertheless, experts emphasize that until the corresponding update is released, users should independently monitor network commands created by the neural network and not rely solely on basic privacy settings.
What This Means for Teams and Developers
The Claude Code incident has become a clear example that autonomous AI agents granted the right to form and execute network requests can inadvertently disclose personal data, even if their task is not related to information transfer. Specialists recommend that teams implement an additional layer of audit: logging and checking all curl and HTTP requests generated by AI tools before they are sent. Furthermore, in working environments, it is advisable to restrict the agent's access to user contact data and use pseudonymous identifiers where technically feasible. Until Anthropic releases an update with the complete exclusion of emails from the model context, such measures remain the only reliable way to reduce the risk of leakage.