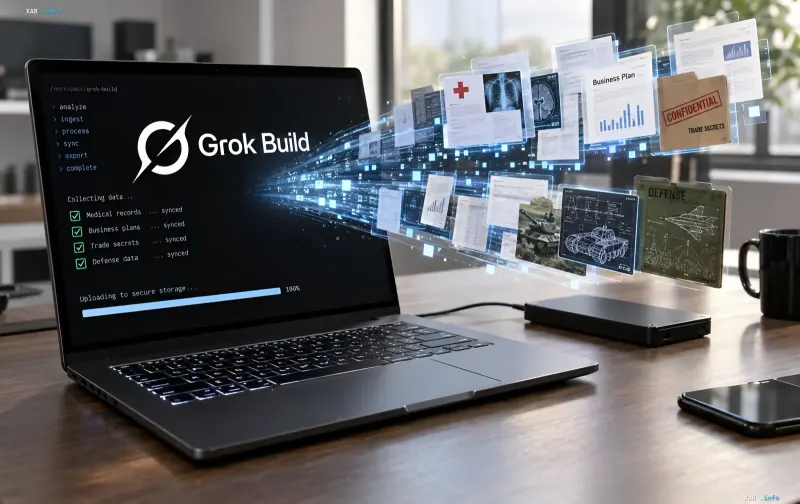
The Grok Build AI platform, developed within the Elon Musk ecosystem, has fallen victim to a massive data leak caused by an architectural error in its link-sharing system. According to researchers from the specialized firm Claroc, over 43,000 unique links to user projects were indexed by public DNS services, with approximately 95 percent of them providing full, default access to applications and the data stored within them. Among the compromised materials were medical records, business plans, trade secrets, and internal documents from defense companies.
The Cause: Random Words in the Subdomain
Grok Build developers created a unique link system using random word combinations to simplify application testing. Initially, it was assumed that only the person to whom the author directly sent the link would have access to the project. However, the platform creators made a critical error: the randomly generated identifiers were placed in the subdomain — the left side of the website address. As a result, public DNS services automatically saved information about every new link, effectively creating an open registry of all created projects. Any user could find these addresses, view the list of projects, and open thousands of them.
Why Other Platforms Were Not Affected
Security specialists emphasize that if the random identifier had been placed in the right-hand path of the URL — as Google, ChatGPT, or Gemini do — passive DNS monitoring would not have been able to record these addresses. It was the architectural decision to place the identifier in the subdomain that turned the internal link system into a public catalog. Experts note that a similar issue with subdomains exists on other AI platforms for code development, making the incident with Grok Build not an isolated case, but a systemic one.
What Exactly Was Leaked: From Medical Records to Defense Schemes
Among the leaked materials, Claroc researchers recorded patient medical records, business plans containing financial data, documents marked "confidential," and trade secrets. A particular outcry followed the discovery of 24 internal SpaceXSI applications containing confidential-labeled sales adaptation plans, sales territory maps, and promotional offers. Defense-related materials, including technical diagrams of military equipment, were also left in the open. According to Claroc, out of more than 43,000 links found, approximately 95 percent provided full access to applications and the data stored within them without any additional authentication step.
Company Response and Rebuttal of Independent Tests
Following public exposure and inquiries by researchers to company management, links to the 24 internal SpaceXSI applications were promptly removed and now trigger an error. Company representatives stated that the applications are "private by default." However, independent tests conducted by Claroc specialists refuted this claim: the vast majority of links provided full public access without any restrictions. Grok Build users are strongly advised to manually change access settings to "invited users only" to avoid repeated data leaks.
Systemic Risk for the AI Ecosystem
The Grok Build incident has exposed a vulnerability characteristic of a whole class of AI platforms where generating unique links via subdomains becomes a source of passive reconnaissance. Security experts urge developers to rethink URL identifier architecture and move random tokens into the URL path rather than the subdomain. Until such fixes are implemented, users of AI code development tools remain at risk: one architectural decision is enough for the confidential data of thousands of organizations to end up in the public domain.