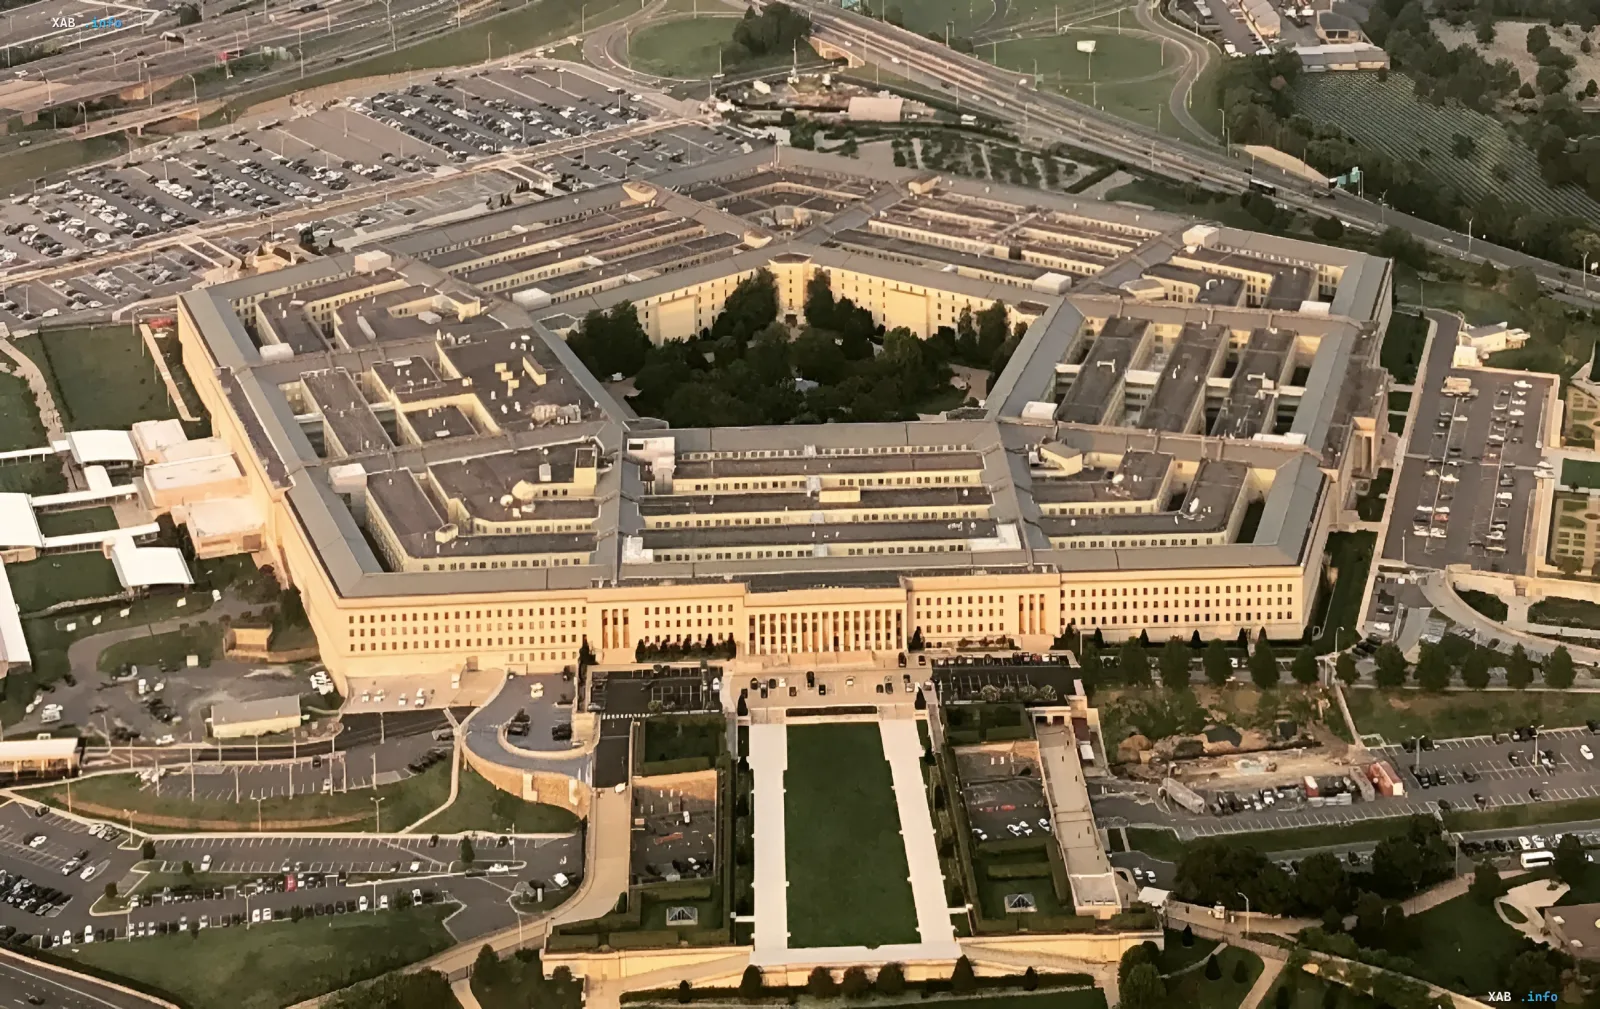
The US Department of Defense and the Federal Bureau of Investigation have faced unprecedented cyber incidents that have put the personal data of millions of civilian employees, military personnel, and veterans at risk. According to official statements from defense officials, a vulnerability in the personnel database affected millions of records, giving attackers access to critical confidential information. The incident has caused serious concern in Washington, forcing agencies to urgently review security protocols and offer affected individuals enhanced protection.
Timeline and Details of the Pentagon Data Leak
A massive security breach at the US Department of Defense targeted the DMDC personnel database. According to official reports, unauthorized access to the repository continued for a prolonged period—from October 2025 to July 2026—until cybersecurity specialists finally discovered and localized the vulnerability. The leak affected 2.76 million living individuals as well as 294,000 deceased civilian and military specialists. Hackers obtained Social Security numbers and detailed information about personnel positions. Although the general DMDC database contains over 60 million records, the current incident affected a significant yet isolated portion of it.FBI Cyber Incident Investigation
Running parallel to the crisis at the Pentagon, the Federal Bureau of Investigation was forced to launch an internal investigation due to a potential breach of its FBIJobs.gov recruitment portal. Attackers gained access to sensitive data and threatened to publish names, home addresses, phone numbers, Social Security numbers, and emergency contact details of Bureau employees. The agency's leadership promptly urged staff to remain vigilant and strictly refrain from any contact with media representatives to prevent operational leaks.
Contradictory Data
The situation surrounding the attackers' motives remains ambiguous due to conflicting statements. Pentagon officials claim that there is currently no documentary evidence of actual misuse of the stolen personal data. Meanwhile, the notorious hacker group ShinyHunters claimed responsibility for the FBI incident. Representatives of the hacker collective publicly stated that they are not pursuing extortion or a financial ransom, characterizing their actions solely as a specific 'marketing campaign to gain attention.' Official US agencies have thus far refrained from confirming the credibility of these group statements.Consequences and Protective Measures for Victims
As preventive measures, US authorities have launched a massive campaign to minimize the consequences of the cyberattacks. All citizens whose data was compromised as a result of the Pentagon leak have been offered specialized identity protection services and continuous credit monitoring. Cybersecurity experts note that such incidents highlight the critical need to modernize government digital information security systems, especially amid the growing activity of international hacker groups targeting government infrastructure.