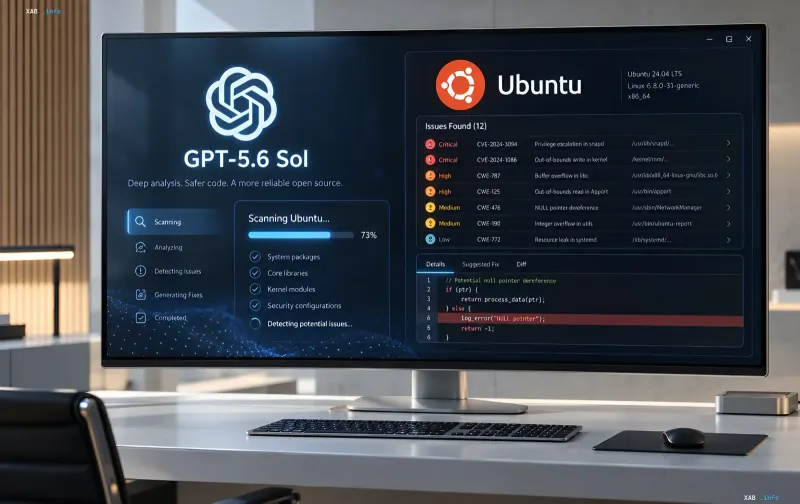
The GPT-5.6 Sol artificial intelligence model has discovered a dangerous vulnerability in the Ubuntu distribution that, if exploited, could allow attackers to gain control over servers. This was reported by Max Justich, CTO of the startup Charge Robotics, who directed the neural network to analyze software code. According to him, the system took just two hours to identify an exceptionally tangled bug that would have been extremely difficult for human analysts to spot manually. The case demonstrates that with AI assistance, even specialists with limited experience are capable of finding serious software errors.
How AI found the tangled bug
According to Max Justich, he pointed the artificial intelligence at the exact code fragment where a problem had been recorded a few years ago. The developer asked the system to look for similar or even more complex errors in this area. The model processed the code and found the vulnerability within two hours, which, by the researcher's estimate, would have been very difficult to detect manually. It was the combination of a known code "spot" and AI's ability to calculate complex scenarios that made it possible to uncover the error hidden within the convoluted logic.
Debian's reaction and patch release
The researcher immediately transmitted information about the vulnerability to the Debian Project team. The developer's specialists quickly prepared and released a security update eliminating the exploit. At the time of publication, there were no reports that attackers had managed to exploit this flaw. Nevertheless, the very fact of the rapid patch release emphasizes that such errors in open-source software require immediate reaction before they become the subject of mass attacks.
OpenAI's broad cybersecurity offensive
Against this backdrop, OpenAI announced a specialized ChatGPT Cyber model designed specifically for cybersecurity tasks. The company also published the results of a large-scale software code review using AI: during the analysis of the Linux kernel, the system found 948 potential issues, and in the Firefox browser, 81 previously unknown vulnerabilities. At the same time, OpenAI emphasizes that these findings still need verification, as not every detected issue is necessarily a real vulnerability. In addition, the company plans to direct $1 billion to support specialists responsible for protecting critical infrastructure, specifically energy grids and water supply systems.
Dual-use: helping experts and a threat from hackers
Experts warn that time to strengthen digital systems' protection is limited: AI models are developing rapidly, and their capabilities to find vulnerabilities are constantly growing. At the same time, these tools are becoming more accessible not only to cybersecurity experts but also to hackers. A particular threat, in their opinion, is posed by open-source versions of models without built-in restrictions—they can be used to search for software weaknesses and prepare cyberattacks.
The window of opportunity is closing
The Ubuntu vulnerability case has become a clear example of how AI is shifting the balance of power in cybersecurity. On one hand, neural networks allow finding and closing flaws in open-source software faster; on the other hand, the same methods are available to attackers. Experts believe that right now, while models' capabilities are not yet mass-available in a "pure" form, developers and infrastructure operators have a window to strengthen their defenses, which will rapidly shrink as technology develops.