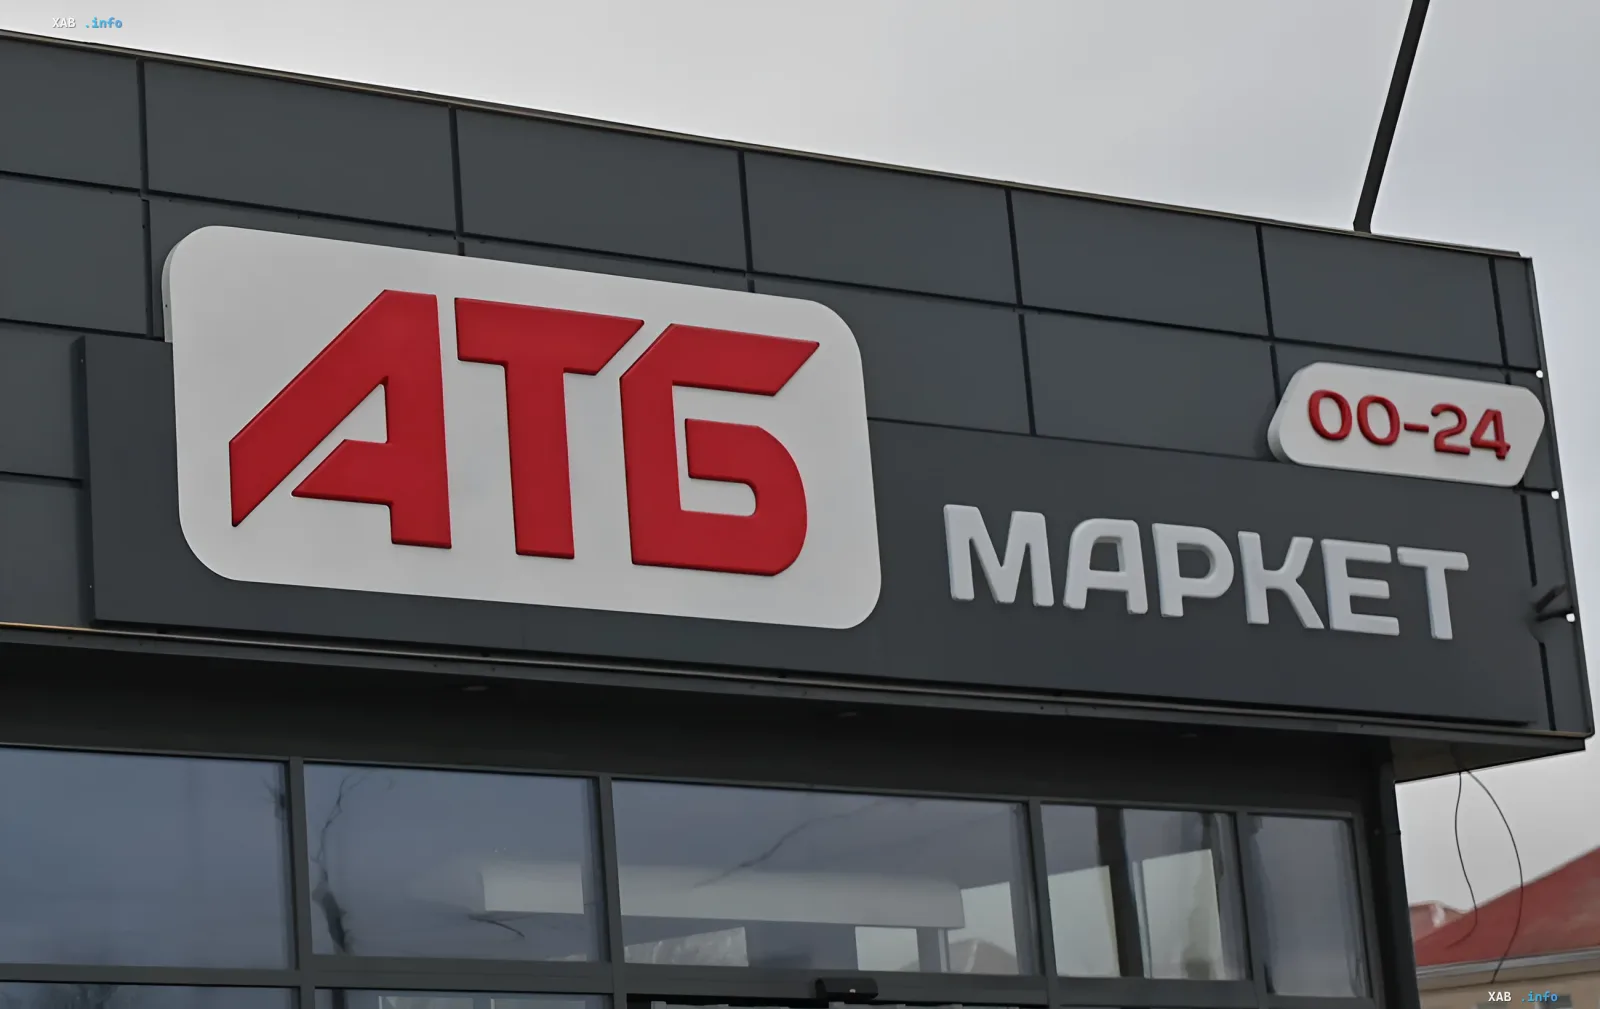
Ukraine's largest retail chain, ATB, has faced a cyber incident that drew significant public and media attention. Unidentified hackers claimed to have breached the company's web resource and demanded a hefty ransom of 400,000 US dollars, threatening to publish confidential user data in the open access. To increase pressure, the perpetrators launched a special countdown timer on the website's homepage and published screenshots allegedly confirming the successful compromise of the systems.
ATB Company's Reaction and Official Denial
The management and press service of the corporation promptly responded to the emerging information security threat. Company spokesperson Serhii Demchenko officially stated that the information spread by hackers about the theft of customer personal data is completely untrue. According to him, the attack was indeed recorded by specialized experts, but the architecture of the corporate website initially does not provide for storing confidential user information, so there is no real danger to citizens.
Contradictory Data
On the one hand, cybercriminals claim to have captured data arrays and demand a payment of 400 thousand dollars in just two hours, backing up their words with generated or stolen file fragments. On the other hand, official ATB representatives insist that the website infrastructure is isolated from user databases, and the resource itself was temporarily shut down by technical services to conduct a detailed audit and eliminate the consequences of unauthorized intervention. Experts note that such actions are often purely blackmail-oriented for the purpose of intimidation and PR.
Cybersecurity Context in Ukraine
This incident occurs against the backdrop of large-scale digital tension in the country. According to official statistics from the governmental computer emergency response team CERT-UA, in the first half of 2026 alone, more than three thousand various cyber incidents were recorded in Ukraine. Intruders are increasingly integrating artificial intelligence technologies to generate malicious code and are purposefully attacking mobile devices of military personnel and civil servants, which requires constant strengthening of digital protection measures.